Control panel security built so one website cannot reach the next
Somewhere on a busy server, a website will run an outdated plugin. Good control panel security decides what happens next. UHost is built so the answer is: very little.
How it is put together
The panel you sign in to has no root.
UHost is two programs. The panel, which answers your browser, runs as an ordinary unprivileged account. Anything that needs root is asked of a separate agent.
- The agent listens only on a restricted local socket, never on the network.
- It accepts a fixed list of typed operations, and never a shell command it was handed.
- It works out every path and Linux account itself from an internal identifier, so a request cannot point it somewhere else.
- Every request is authorised on the panel against the resource it touches.
signed-in requests
typed operations over a local socket
configures
Every website
Protection that is on before you think to turn it on.
Its own account
Each website runs as its own Linux user with its own PHP pool and socket, and cannot read another website's files.
Mail kept apart
Mail is stored under a dedicated account outside the website, so a compromised website cannot read its customer's mailboxes.
No scripts from uploads
Nothing runs from a folder an application writes to, so an uploaded file cannot become a program.
PHP cannot run commands
The functions a web shell needs are switched off, which is what most compromised websites are used for.
Scanners turned away
The paths vulnerability scanners ask for, and files that are never web content, are refused outright.
Password guessing slowed
Repeated sign-in attempts against a website's login pages are rate limited, per website.
You and your customers
Signing in, and staying in control.
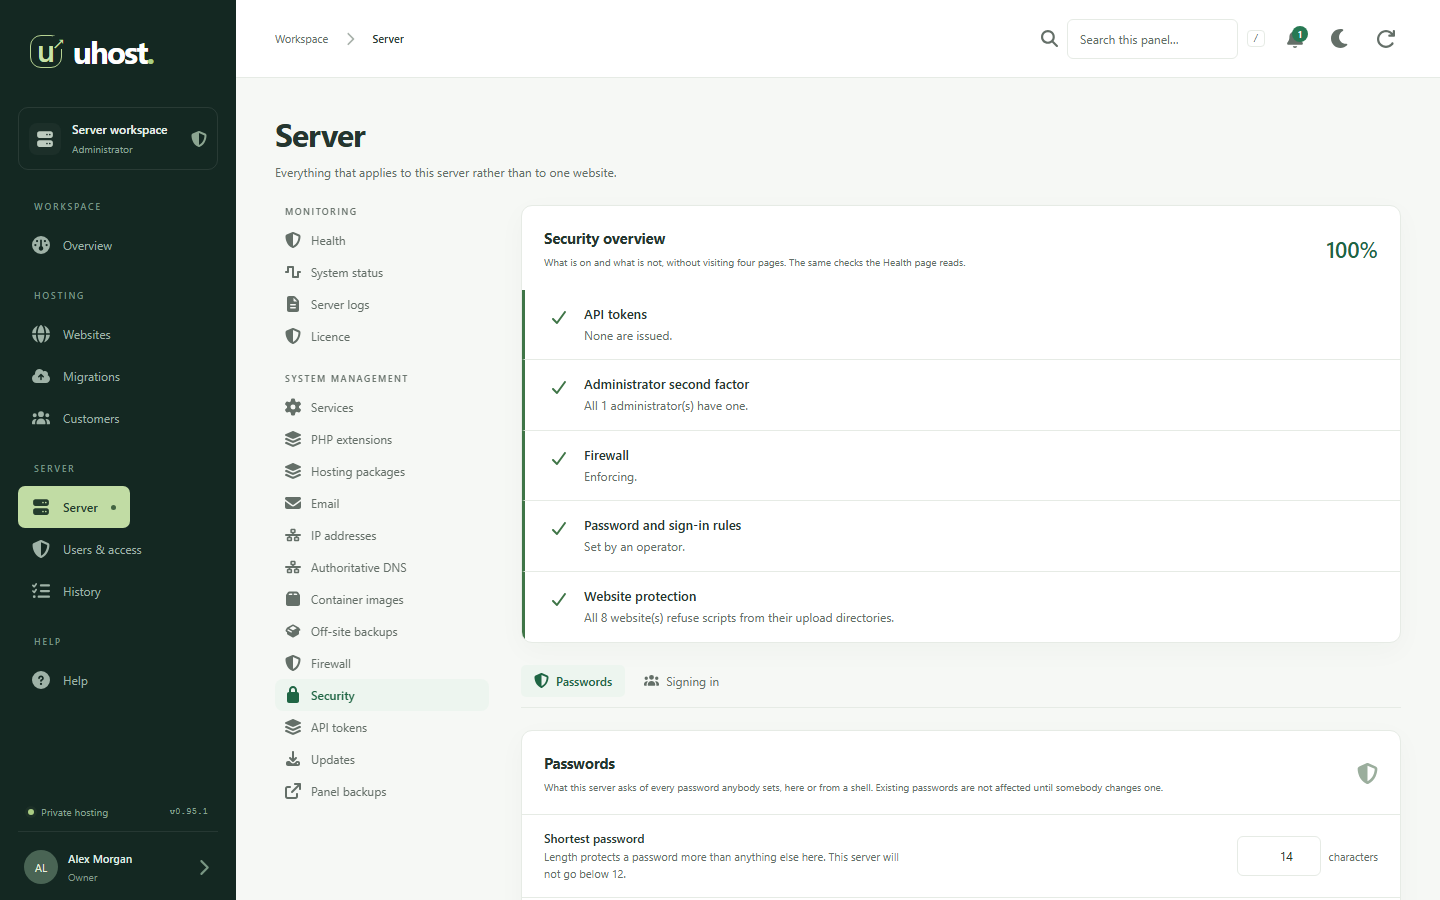
Two-factor sign-in
Codes from any authenticator app, with single-use recovery codes stored only as hashes.
Strong password storage
Passwords are hashed with Argon2id. There is no default password: the first account is created with a single-use token.
Rules for the whole server
Set password and sign-in requirements for everybody who signs in to your server.
A firewall that will not lock you out
A rule that would cut off the address you are connecting from is refused by name, and the ports the server must answer on are kept open.
Signed updates
An update is refused unless UHost signed it. It installs when you press the button, snapshots the panel first, and tries to put everything back if it fails.
Your hosting outlives your licence
A licence that runs out puts the server on the free plan. It never takes a website, mailbox or zone offline.
UHost's security review so far was carried out by the people who wrote it, and says so. An independent review is planned. UHost is not yet version 1.0.
Your servers, without the per-account bill.
UHost launches 13 October 2026: the whole panel free for one website, and Pro for unlimited websites on a server.